AI & Platforms / Identity & security

Make sure a stolen password isn't enough to get into Microsoft 365.

We set up Microsoft Entra ID, Conditional Access and Microsoft Defender across every account, admins included. Copilot runs on each person's own sign-in, and meeting rooms and Teams phones get rules written for them.

Talk to us about identity and security

Most identity attacks try to guess a password.

Microsoft's Digital Defense Report 2025 found that more than 97% of identity attacks were password spray or brute force: a few common passwords tried against many accounts, or many passwords tried against one.

With multifactor authentication (MFA), a guessed password isn't enough on its own, and passkeys or Windows Hello let people sign in without typing one. The harder part is covering everything: every account, the admins, the old sign-in methods nobody switched off and the meeting rooms that sign in by themselves.

Sign-in rules that check the device as well as the person.

Conditional Access in Microsoft Entra ID tests each sign-in against rules you set: who's signing in, whether their device is managed and up to date, where they are and how risky the sign-in looks.

We write the rules, try them on a small group, then switch them on for everyone. Admin accounts get stricter rules, and Privileged Identity Management gives people admin rights only when they need them.

See how we match Microsoft 365 plans to each job

Meeting rooms and Teams phones sign in too.

A Teams Room signs in to Microsoft 365 with its own account, and nobody's in the room to answer an MFA prompt. Microsoft doesn't support requiring MFA on Teams Rooms on Windows, and a rule that forces a fresh sign-in at set intervals will sign a room out.

So rooms, room panels and Teams desk phones get rules written for them, such as allowing sign-in only from a managed, compliant device on your own network. The room stays signed in, and someone who learns its password can't use it from home.

See what a room refresh covers
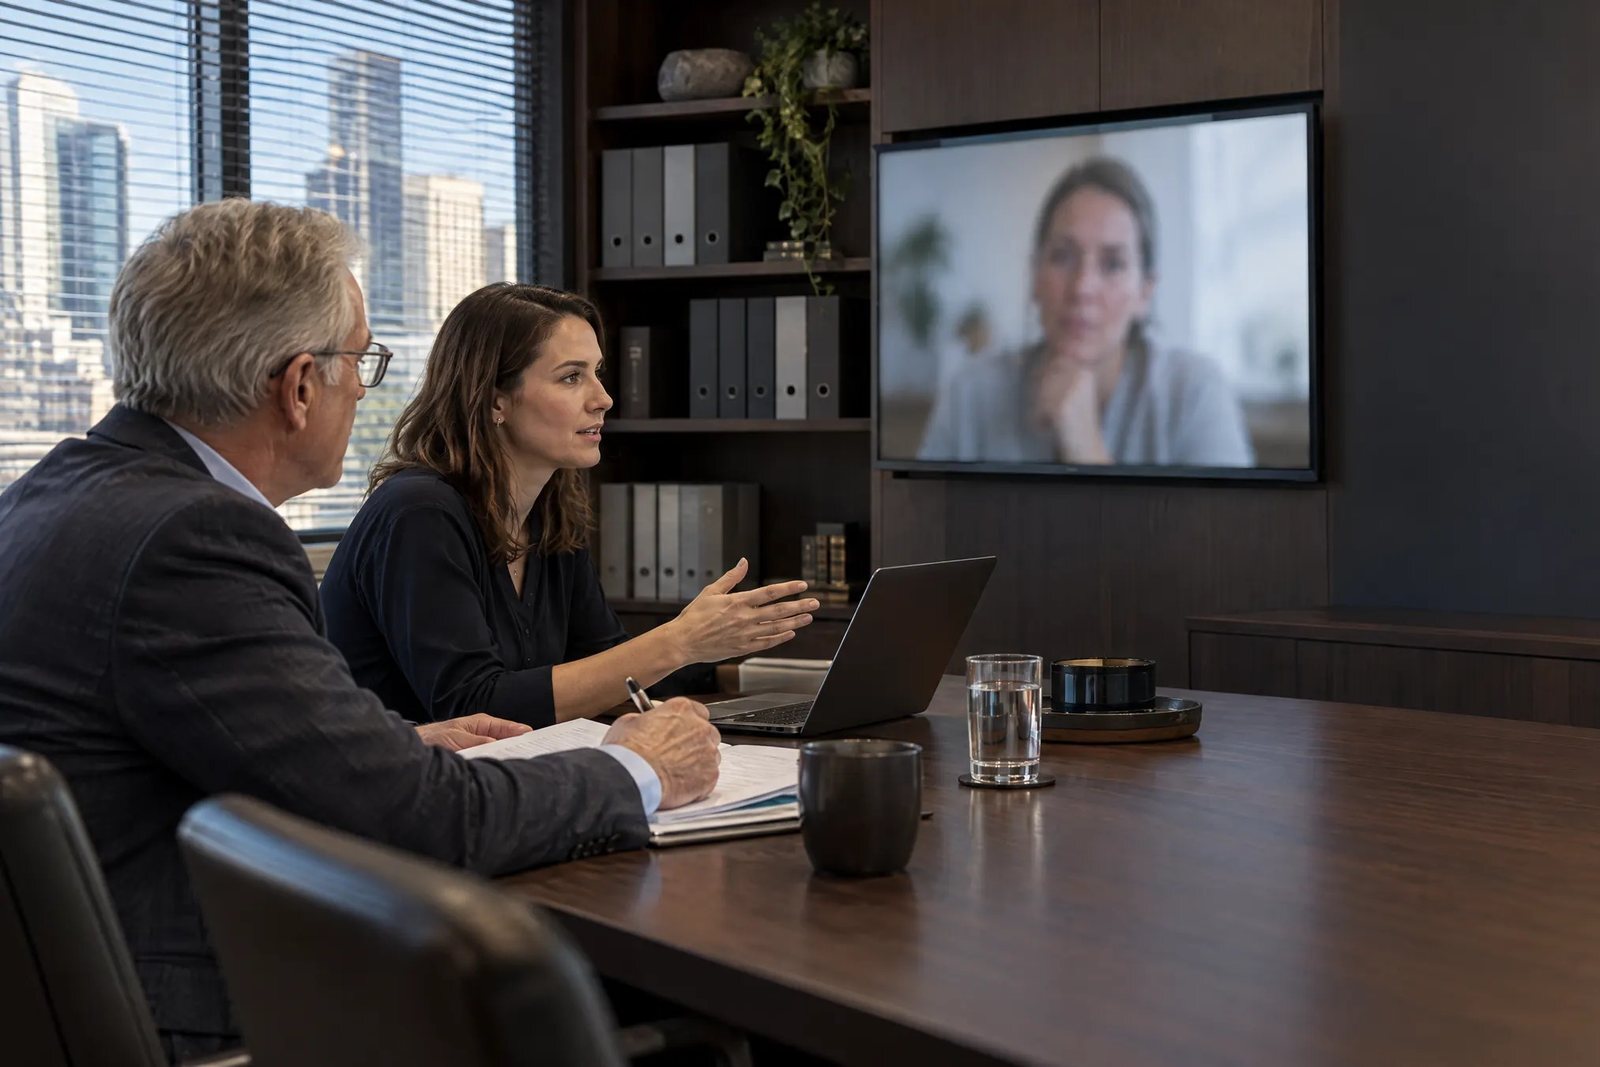
Two advisers talk with a client who appears on the meeting-room screen. Illustrative image.

Copilot works with the same sign-in and the same permissions.

Copilot answers from the Microsoft 365 content the signed-in person already has permission to open. Whoever signs in as that person can ask it the same questions.

That's why we tighten sign-in and admin access before Copilot reaches everyone, then check who can open what.

See how a Copilot readiness assessment works
A woman reads her laptop late at night in an almost empty office. Illustrative image.

What we check in your Microsoft 365 security settings

When we review your Microsoft 365 setup, we start with settings like these.

  • Old sign-in methods, such as legacy authentication, that can't use MFA
  • MFA on every account, admins first
  • Who holds admin rights, and whether they need them every day
  • Microsoft Defender's preset security policies on sensitive accounts
  • Automatic forwarding of email to outside addresses
  • SPF and DMARC records, which help stop fake email that claims to come from your domains
  • Sharing settings in SharePoint, OneDrive and Teams

Questions about identity and security

Do we need to fix identity before rolling out Copilot?

Fix the biggest gaps first: MFA on every account, admin rights and old sign-in methods. Copilot doesn't change who can open what, but it finds whatever an account can open much faster.

How does this map to the Essential Eight?

Two of the eight strategies are about identity: multi-factor authentication and restricting administrative privileges. We set up the parts of both that sit in Microsoft Entra ID, matched to the maturity level you're aiming for.

Do we need extra licences?

Conditional Access comes with Entra ID P1, which is part of Microsoft 365 E3. Risk-based sign-in rules and Privileged Identity Management need Entra ID P2, which comes with E5 or as an add-on. We'll check what you already have before suggesting more.

Will people have to sign in more often?

Usually not. Single sign-on, passkeys and Windows Hello mean fewer password prompts, and Conditional Access can ask for a second check only when a sign-in looks unusual.

Do you look after it once it's set up?

Yes. Through M-Serv, our managed support, we keep the rules current as people join, change roles and leave, and as you add rooms and devices.
Start with how your people sign in today.

Tell us roughly how many accounts, admins and meeting rooms you have, and how people sign in now. We'll call to propose a review of your Microsoft 365 security settings, ending with a prioritised plan for fixing what we find. We agree its scope and cost with you before it starts.

Talk to us about identity and security